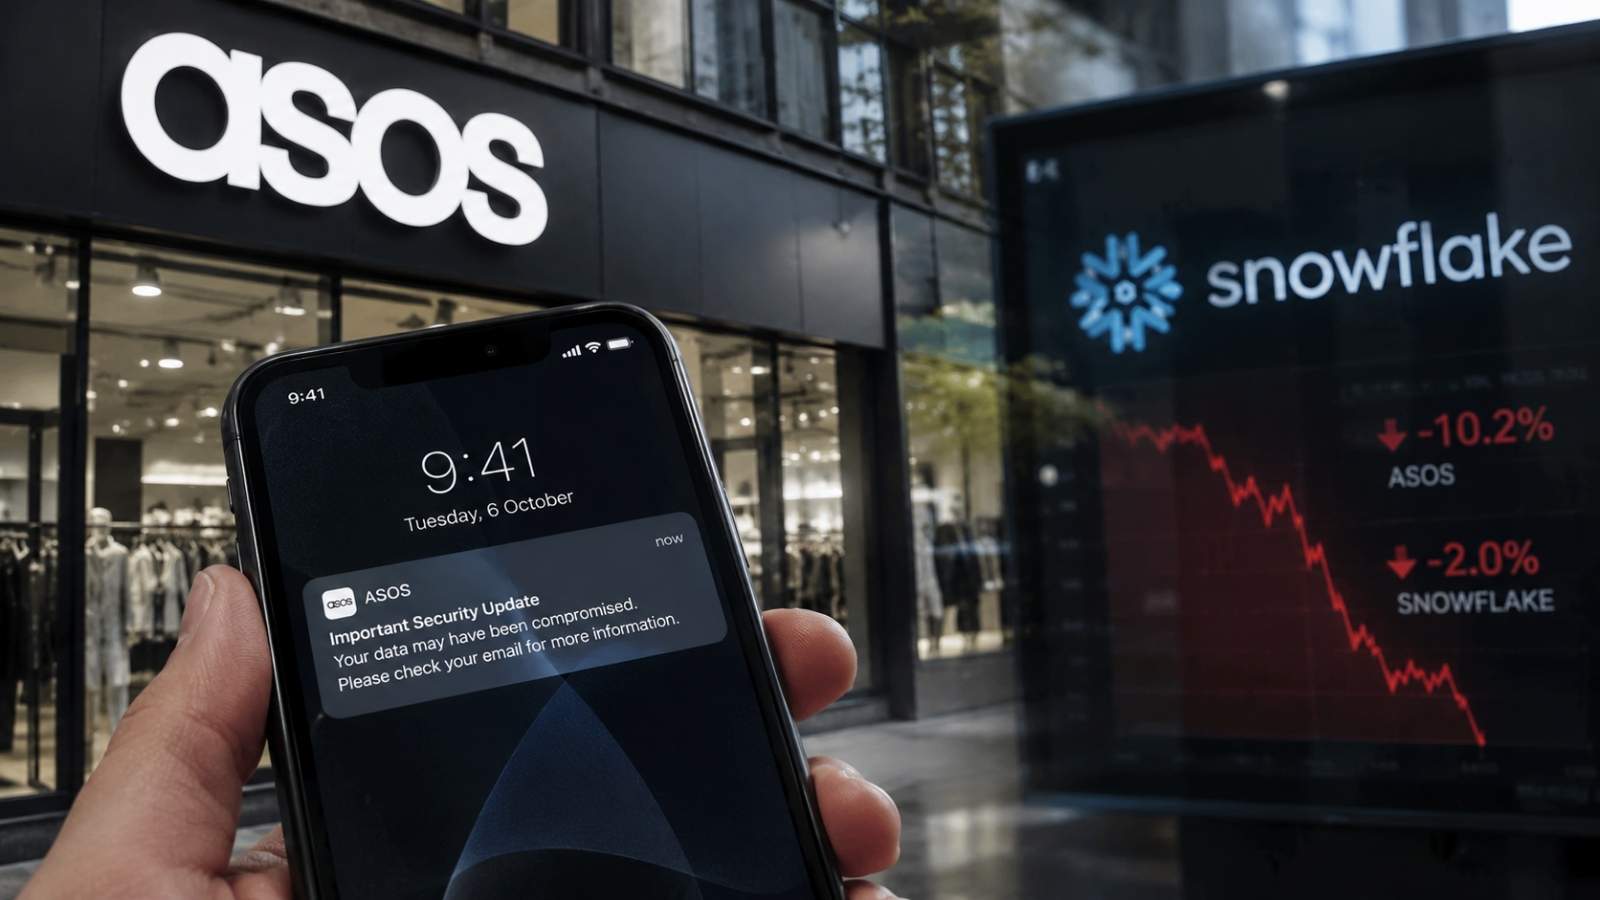
The ASOS hack notification sent shares in both ASOS and cloud data provider Snowflake sliding on Tuesday, after a threatening push alert told customers their data had been breached.
ASOS Hack Notification: What the Push Alert Said
The ASOS hack notification arrived without warning on Tuesday morning, as users of the fast-fashion retailer’s app received a push alert claiming hackers had fully compromised the Snowflake instance used to store ASOS customer data. The message was addressed to the retailer’s Data Protection Officer and IT staff, warning the company to engage with the attackers or risk having the stolen data leaked, and pointed recipients toward a Telegram channel for further contact.
The notification spread quickly on social media after users began sharing screenshots, with reactions ranging from alarm over payment details to dark humor about the incident. As of Tuesday morning, ASOS had not confirmed or denied the extent of any breach, and the company is yet to issue an official statement.
Why the Snowflake Connection Is Raising Alarm
Snowflake, the cloud-based data storage and management platform named in the notification, has previously been linked to a wave of high-profile breaches affecting dozens of major companies, a history that is adding weight to the attackers’ claims this time. ASOS uses Snowflake to store and manage large volumes of customer information, making any confirmed compromise of that instance a potentially significant exposure for the retailer’s customer base.
ASOS and Snowflake Shares Fall After the Hack Claim
Shares in ASOS fell sharply on Tuesday, dropping as much as 10.2% during the session to a low of 435.5p after opening at 485p, a decline that stood out against a broader FTSE 250 index that traded higher on the day. Snowflake’s own US-listed stock slipped around 2% in early trading, as investors weighed the reputational and security implications for the cloud platform itself.
ASOS has around 17 million customers across more than 150 countries and reported revenue of £2.5 billion in 2025, meaning a confirmed breach could carry significant regulatory and reputational consequences. Under UK data protection law, companies are required to report confirmed data breaches to regulators within three days and to notify affected customers directly in cases assessed as high-risk.
Beyond the announcement
Cybersecurity commentators have cautioned that claims made directly to a company via an in-app notification, rather than through a confirmed breach disclosure, can sometimes overstate the actual scope of an intrusion. Even so, the method of delivery — pushing the threat straight into ASOS’s own customer-facing app — is itself notable, since it suggests the attackers may have had deeper access to ASOS’s systems than a typical external email-based extortion attempt would require.
Analysis
Until ASOS issues an official statement confirming or denying the extent of any breach, customers are left with more questions than answers about what data, if any, has actually been exposed. The three-day regulatory reporting clock under UK law means an official update is likely within days rather than weeks. For Snowflake, the incident revives scrutiny of its security track record following previous large-scale breaches tied to its platform, a pattern that is likely to keep pressure on both companies’ share prices until the facts of the ASOS hack notification are fully established.
Explore more expert insights, leadership stories, and business strategies at GlobeVox Leaders